Disposable Email Policy for Websites: Acceptance and Blocking Rules
Website owners should start with the harm they need to prevent, then use the narrowest control that addresses it. Combine rate limits and behavior signals with clear error messages and a false-positive path. Require durable email only when the product truly needs future contact or recovery.
Blocking every disposable or unfamiliar email domain is a blunt anti-abuse control. It can reduce some automated sign-ups, but it also rejects privacy-conscious people, forwarding aliases, new business domains, and legitimate users who do not want a primary address added to another database.
Use this as a product-control review: name the abuse cost, test the signal, measure false positives, and give legitimate users a proportionate way forward.
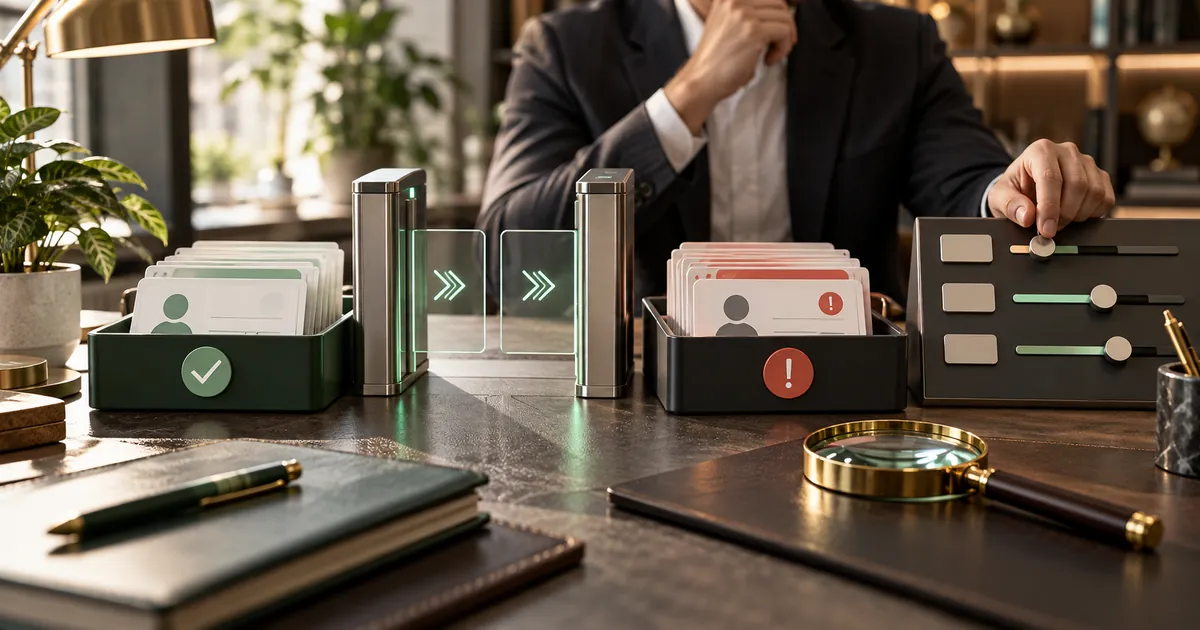
How blocking systems identify an address
A site may compare the domain against commercial or community lists, inspect MX and DNS patterns, score domain age or reputation, limit repeated sign-ups, or review behavior after registration. Some systems reject the form immediately; others accept the address but suppress mail or request stronger verification.
These are risk signals, not proof. New business domains, privacy aliases, school domains, and small mail providers can be caught by broad rules.
Lists also age. A domain can change purpose, a provider can add or remove domains, and a cached result can outlive the data that justified it. Record the data source, lookup time, and rule version so a rejection can be explained and corrected. Treat lookup failures as an operational state, not automatic proof that the user is abusive.
Detection should not collect more personal data than the decision requires. In many cases the domain, request context, and abuse signals are sufficient. Avoid sending a complete address to additional vendors unless the product has a clear need, an appropriate agreement, and transparent handling rules.
Decide whether durable contact is actually necessary
- Delivering receipts, safety notices, support replies, or service changes.
- Recovering an account and warning about suspicious activity.
- Enforcing one-person offers, trials, votes, reservations, or rate limits.
- Reducing fake accounts that send abuse or consume costly resources.
- Meeting recordkeeping, identity, age, payment, or regulatory obligations.
Whether each reason is proportionate depends on the service. A simple download form has a different need than a bank.
Write the harm in measurable terms before selecting a control. Examples include trial consumption, messaging abuse, costly resource creation, chargebacks, or inability to deliver a required receipt. “We want real users” is too vague because an email domain does not establish that a person is genuine.
Then ask whether email durability actually prevents that harm. Rate limits can address repeated sign-ups, delayed privileges can reduce immediate abuse, and payment or identity checks may already cover higher-risk actions. Requiring a permanent address adds friction and another stored identifier, so it should solve a defined product need.
Design a fair fallback
- Explain why a durable address is required instead of showing “invalid email.”
- Let the user correct a typo without losing the rest of the form.
- Provide a review path for normal domains and privacy aliases that are misclassified.
- Offer another proportionate verification method when email durability is not essential.
- Log the rule and provider version that caused a rejection so support can investigate.
A useful rejection message names the requirement without accusing the user. For example, explain that the account must receive future security and recovery mail, then offer a correction field and a support route. Keep the rest of the submitted form intact so one address decision does not force the person to repeat unrelated work.
Support needs enough evidence to reverse a false positive. Show staff the matched rule, source version, and timestamp, and let them approve a legitimate domain without disabling the entire control. Review overrides later so recurring classification errors improve the policy.
Why list-only blocking becomes an arms race
Rotating to another disposable domain may work briefly, but it creates an arms race. The new domain can be listed, legitimate users lose delivery, and the website increases friction for everyone. It also does nothing to solve account recovery.
For users who need a continuing relationship without exposing a primary address, a unique forwarding alias gives the site a durable route and gives the user a targeted off switch.
Blocking by domain alone also encourages constant list refreshes while attackers move to ordinary mailbox providers. This shifts cost toward maintenance and false positives without addressing device, payment, network, or behavior patterns that may be closer to the actual abuse.
A list can still be one input. Use it to adjust friction or request another proportionate signal, then combine it with account behavior. Do not let one vendor response silently become a permanent account ban.
Use layered controls and test the user experience
Site owners can combine rate limits, abuse monitoring, proof of work, delayed privileges, payment verification where appropriate, and behavior-based controls. They can explain why durable contact is needed and allow recognized alias services. A narrow control tied to actual harm is often more effective than rejecting every unfamiliar domain.
Developers should also test error copy and false-positive recovery. The test email guide includes cases for accepted, rejected, and delayed sign-up mail.
Roll out the policy with measurable outcomes. Track completed sign-ups, confirmed abuse, support contacts, reversals, delivery failures, and the domains most often overturned. Compare those numbers with the stated harm. A lower sign-up rate alone does not prove the control is working.
Test provider timeouts and stale data as well as positive matches. Decide whether a lookup outage should allow the sign-up, add a review flag, or delay a high-risk action. The fallback should match the product consequence and should never expose an internal vendor error as a vague “invalid email” message.
Policy review questions
How does a website know an email is disposable?
It may use domain lists, DNS and MX signals, reputation data, registration patterns, or a third-party risk service.
Should every website reject disposable email?
No. The control should match a concrete risk. A low-risk download and a regulated financial account do not need the same identity and recovery policy.
Can a forwarding alias also be blocked?
Yes. Filters can misclassify alias domains or reject them by policy. Contact support or use another legitimate durable address.
Should I keep trying new temp domains?
No. Repeated attempts can trigger stronger anti-abuse controls and may violate the site's rules. Use an appropriate durable address or do not use the service.
Product-policy and false-positive guidance reviewed 2026-11-02.